Vernam: give your next agent a key it can't leak. Your agents use your keys. They never see them.
Give your next agent a key it can't leak
Your agents use your keys. They never see them.
Vernam hands Claude Code, Codex and every other agent a placeholder token. A proxy on your machine swaps in the real key, but only for the API that key belongs to. Every request is logged.
// one session, played back
Watch an agent try
It prints its key and gets a placeholder. It calls OpenAI and the real key is added on the way out. It sends the Stripe token somewhere it shouldn't and gets a 403.
- POSTapi.stripe.com/v1/refundsKey addedcodex STRIPE_SECRET_KEY
- GETapi.github.com/repos/acme/billing/pullsKey addedcodex GITHUB_TOKEN
Three commands. No code changes.
Your agent keeps calling the same SDKs with the same variable names. The values it holds just don't work anywhere else.
- 1
Put your keys in the vault
vn add stores each key encrypted on your machine, pinned to the API it belongs to.
$ vn add STRIPE_SECRET_KEY --preset stripe - 2
Run your agent through Vernam
The agent gets placeholder tokens, and its SDK base URLs point at a proxy on 127.0.0.1.
$ vn run -- codex - 3
The real key is added on the way out
A token on its own route gets the real key. On any other route it's refused before leaving your machine.
$ vn log
// gilbert vernam, 1917
Old maths for new agents
Vernam invented the one-time pad: combine a message with random noise and what's left is useless to anyone without the pad. Your agent holds the noisy half. The proxy holds the rest.
Built for agents that run on their own
Coding agents read files, run commands and follow instructions they find on the web. Vernam assumes one of those instructions will be hostile.
Keys pinned to their host
A Stripe key only ever reaches api.stripe.com. A prompt injection can't send it anywhere else.
Agents see placeholders only
Printing the environment or reading .env turns up vn_ tokens that are useless outside the proxy.
We never hold your secrets
Keys live in an encrypted vault on your machine. The dashboard gets hosts, paths and status codes.
Every request, logged
See which agent called which API with which key, live, across your whole team.
Policies per keyIn preview
Allow reads, block refunds, cap requests per minute. Blocked calls wait in a review queue.
End a session instantly
Something looks wrong? End the agent's session and its placeholders stop working at once.
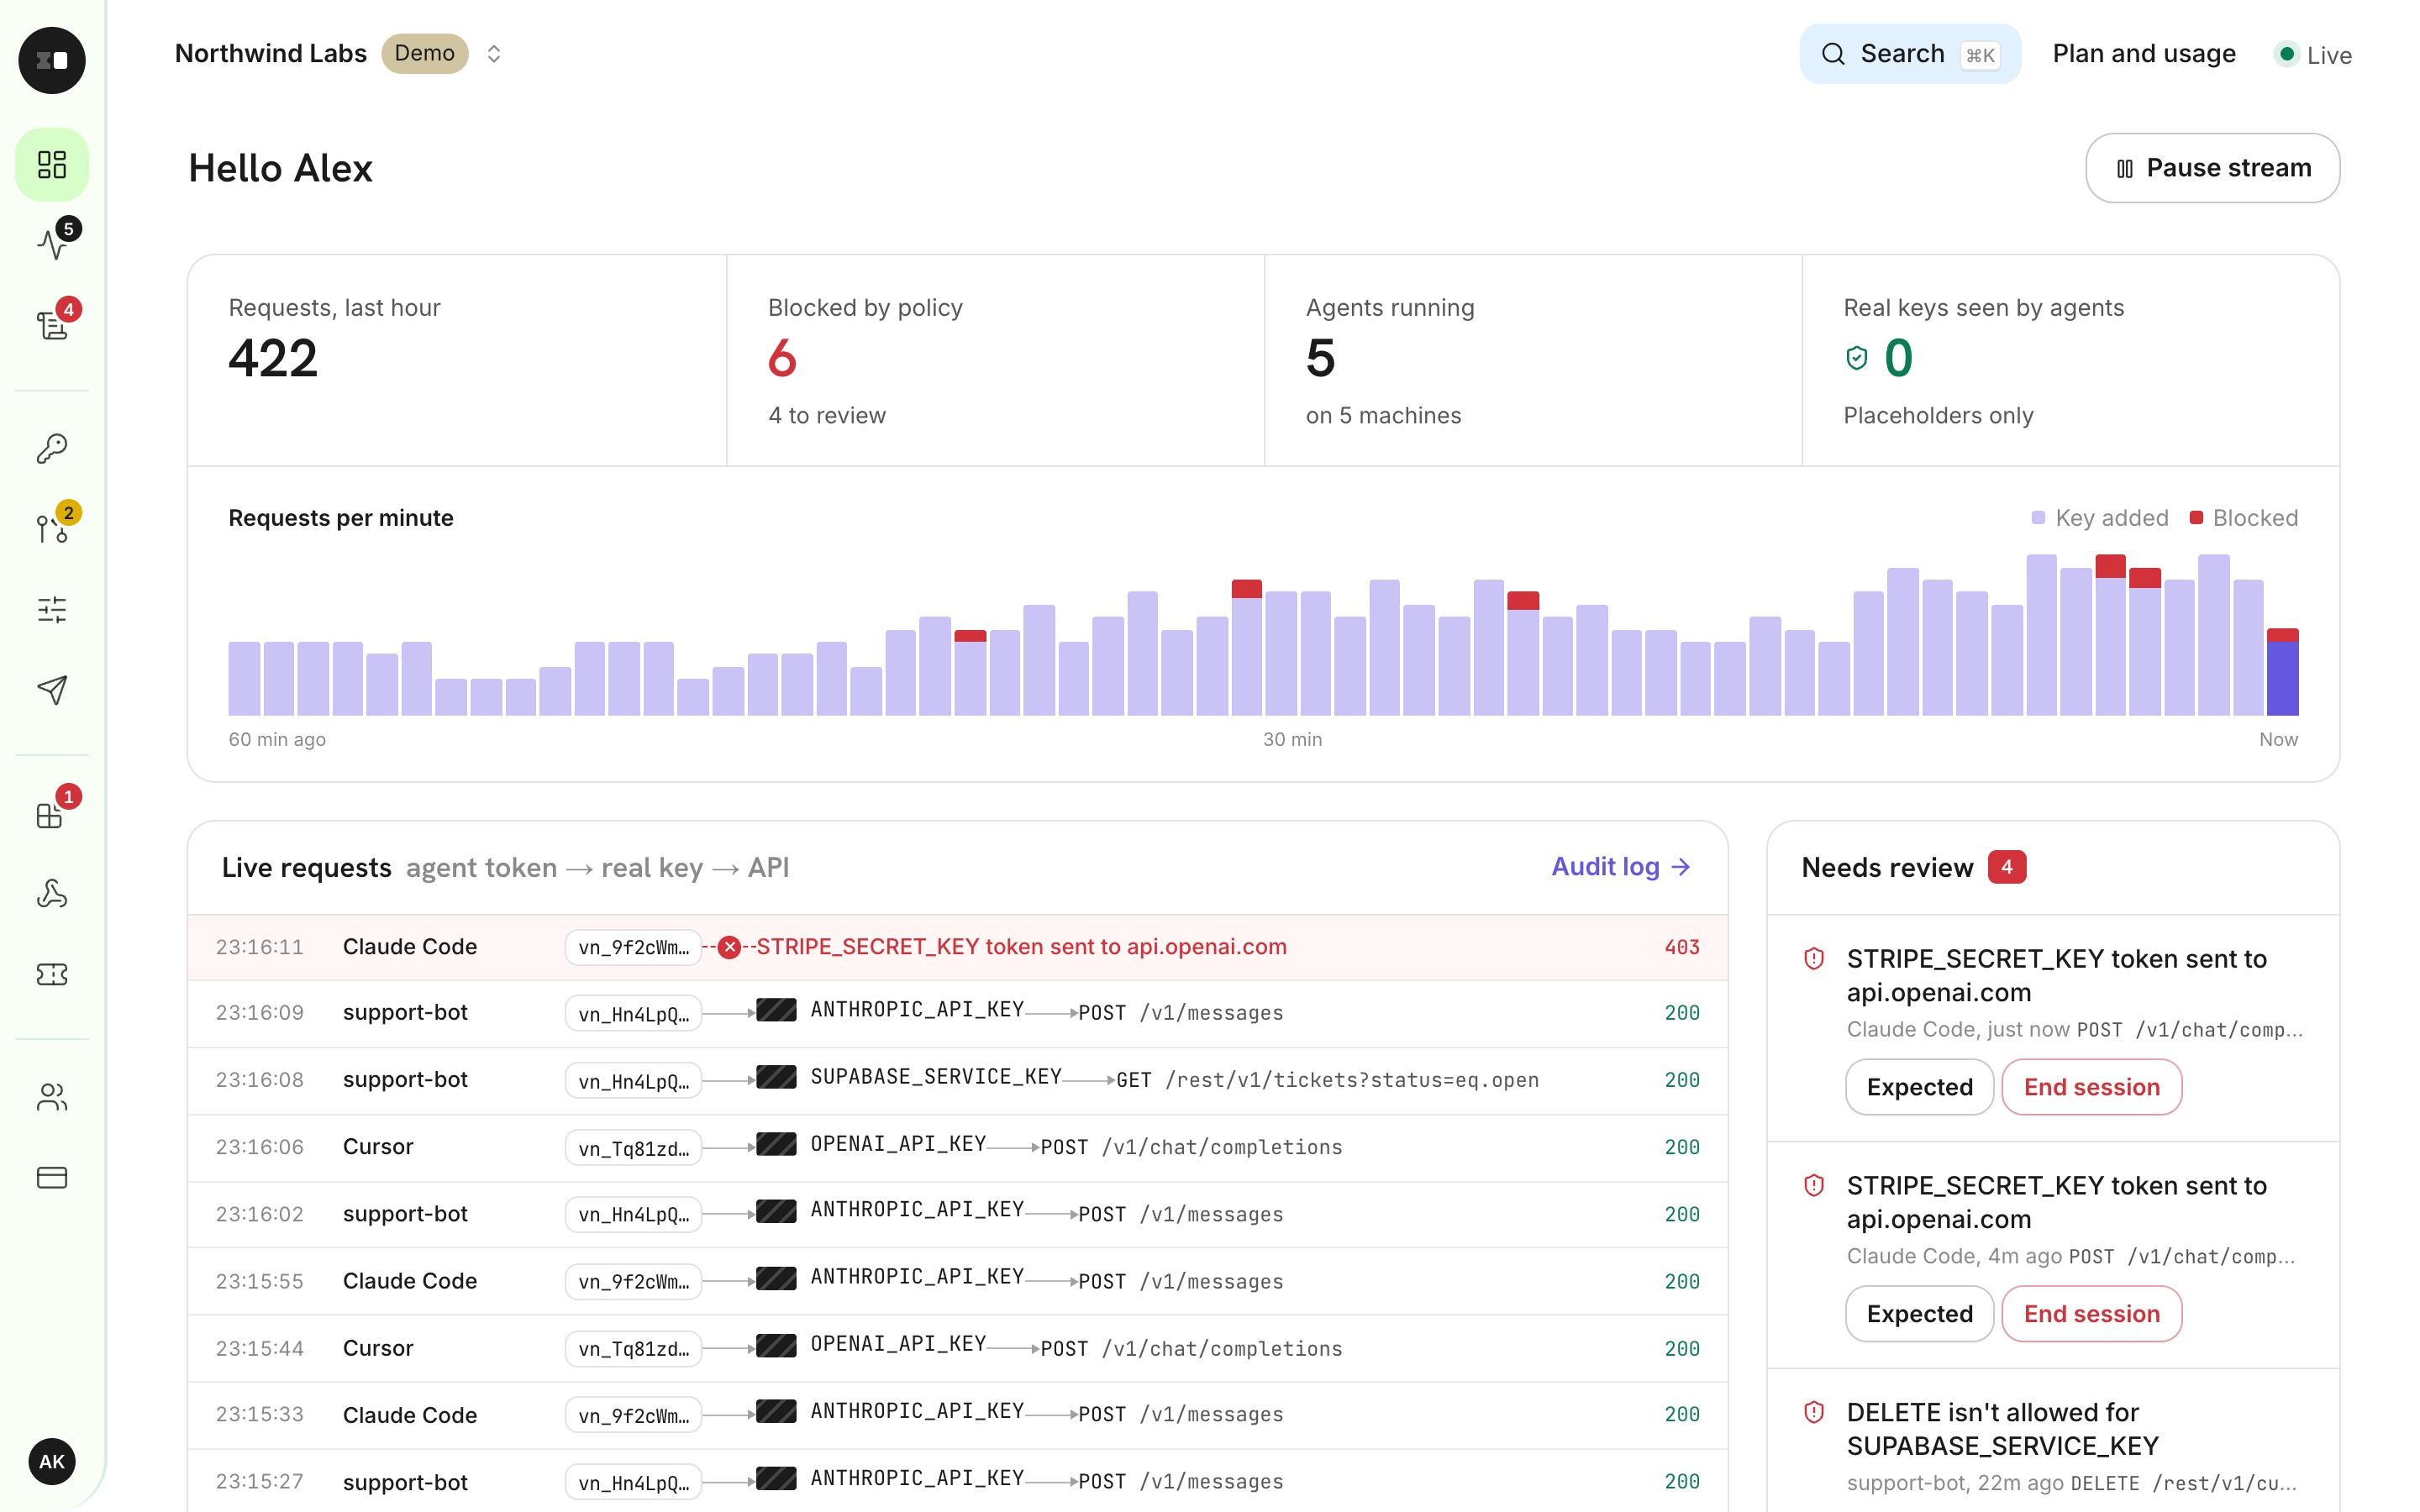
Every agent on your team, in one live log
Run vn login once per machine. Requests stream into a shared dashboard: who ran what, which key it used, what got blocked. Values never leave the machine.
Secrets managers hand the agent the key
A secrets manager is great at getting a key into a process. Once it's there, an agent can print it, paste it or post it anywhere. Vernam never puts it there.
| .env file | Secrets manager | Vernam | |
|---|---|---|---|
| Agent can read the real key | |||
| Key works against any host | |||
| Log of each request an agent makes | |||
| Cut off an agent mid-session | |||
| Secrets stored on someone else's server |
// threat model
Assume the agent turns on you
Vernam is built for the worst case: an agent running as you that has just read a malicious README. Here's what it gets.
Priced per team, not per request
Brokered requests are unlimited on every paid plan.
Business
- Unlimited agents
- Key rotation for OpenAI, Stripe and GitHub
- SSO and Slack approvals
Questions
Do you store my API keys?+
No. Keys live in an encrypted vault on your machine and only exist in memory while the vault is unlocked. The team dashboard receives key names, hosts, paths and status codes.
Does it slow requests down?+
The proxy runs on 127.0.0.1 and swaps a header on each request. It doesn't change where the request goes, so the API's own latency dominates.
Do I have to change my code?+
No. vn run sets the usual variables, like OPENAI_API_KEY and OPENAI_BASE_URL, so official SDKs pick up the placeholder and the proxy without changes.
Which APIs work today?+
OpenAI, Anthropic, Stripe and GitHub have presets. Other HTTPS APIs work with a custom target, as long as your SDK reads a base-URL variable.
Do I need the dashboard?+
No. The CLI works on its own and sends nothing anywhere. Run vn login when you want your team's requests in one live log.